A .onion address is the 56-character string that identifies a dark web site. It looks random because it is the service's cryptographic public key encoded directly into the address, rather than a human-chosen name. Connecting to it proves you reached the genuine service, with no certificate authority to trick.
- An .onion address is a public key, encoded — not an assigned name
- It proves its own authenticity: no authority to impersonate
- Modern v3 addresses are 56 characters; old 16-char v2 is dead
- It looks like noise because it's a key fingerprint
- One wrong character is a phishing clone — always verify in full
Anyone who sees a dark web address for the first time asks the same question: why does it look like someone fell asleep on the keyboard? The answer is genuinely elegant, and it explains both the dark web's greatest security strength and its most common way of robbing people.
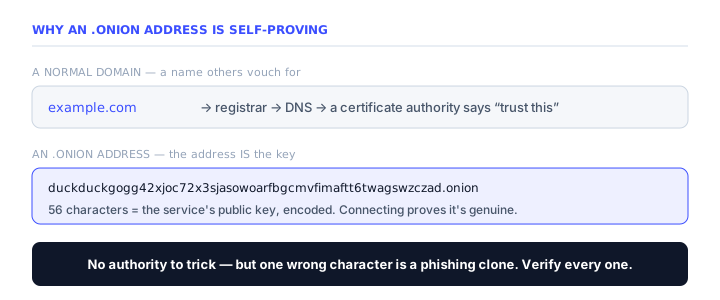
How a normal address works
A domain like example.com is a human-chosen name. For it to reach the right server, trusted authorities vouch for it: a registrar records ownership, DNS translates it, and a certificate authority issues the padlock. It works — but every one of those authorities is a party that can be compromised or tricked.
How an onion address works
An onion service throws that model out. Its address is derived directly from a cryptographic public key — the 56 characters you see are that key, encoded. The address isn't a name pointing at the service through intermediaries; the address is the service's identity, mathematically. When you connect and it responds, the cryptography proves you've reached the genuine service, with no authority to fool.
Why it looks like noise
The randomness is the key showing through. Because the address is cryptographic material, it can't be a chosen word — it's essentially a key fingerprint, and fingerprints look like noise. This also means addresses can't be casually guessed or brute-forced into a meaningful name.
The strength that becomes the danger
Because no human can read 56 random characters, almost nobody checks them — and phishing clones exploit exactly that, registering look-alike addresses one character off the real one. The cryptography is unbreakable; the human reading it is not. Always verify the full address, never just the memorable-looking ends.
v2 vs v3
You may see references to shorter, 16-character onion addresses. These are the old version-2 format, now deprecated and defunct — they no longer load. Modern version-3 addresses are the 56-character strings with far stronger cryptography. A 16-character onion address is dead.
Frequently asked questions
What is a .onion address?
A .onion address is the 56-character Base32 string that identifies a Tor onion service. It encodes three pieces of data: a one-byte version field, the service’s 32-byte Ed25519 public key, and a two-byte checksum. Because the address is derived directly from the public key, connecting to it cryptographically proves you reached the genuine service, with no certificate authority involved.
Why do onion addresses look random?
Because the address is a compact encoding of cryptographic key material, not a human-readable name. Ed25519 public keys are 32 bytes of random-looking data, and after adding the version and checksum bytes, the whole 35-byte record is converted to Base32 using only the letters A–Z and digits 2–7. The resulting 56 characters have no linguistic pattern, which prevents casual guessing and makes impersonation by guesswork unrealistic.
Why are onion addresses so long?
Version 3 onion addresses are 56 characters because they carry 35 bytes of data: 1 byte for the version, 32 bytes for the Ed25519 public key, and 2 bytes for the checksum. When those 35 bytes are encoded in Base32 without padding, they produce exactly 56 characters. The older v2 addresses were only 16 characters because they used a truncated SHA-1 hash of an RSA-1024 key, which offered much less security and is now deprecated.
Are .onion addresses safe?
The address system itself is cryptographically strong: it uses Ed25519 signatures and a self-authenticating design, so an attacker cannot impersonate a service without its private key. The main weakness is human verification. Because 56 characters are hard to read, phishing sites often rely on visually similar characters or truncated copies in links. Always compare the full address from a trusted source, character by character, and remember the Base32 alphabet excludes 0, 1, 8 and 9, so any .onion address containing those digits is invalid.
What is the difference between v2 and v3 onion addresses?
Version 2 addresses used 16 characters based on a SHA-1 fingerprint of an RSA-1024 public key; they were deprecated due to weak cryptography and are no longer reachable in modern Tor. Version 3 addresses use 56 characters and are based on Ed25519 public keys, a version byte, and a checksum. The move to v3 also improved scalability and resistance to enumeration: v3 services can publish many more descriptors and use stronger authentication.